Executive Summary
On October 7, 2026, CrowdStrike published an analysis of a possible threat actor, drawing on a Claude Code markdown document retrieved from the server at 38.244.50[.]120. Building on that analysis, Logpresso investigated additional information related to the threat actor. Notably, the Chinese national identified as the person behind YY520CN has denied any involvement in the hacking, claiming that their mobile phone number had been misused (in Korean). We therefore assess that more information is needed to pinpoint the threat actor.
Using publicly available leads from services such as Telegram and GitHub, Logpresso identified the Telegram account YY520CN as a community supervisor (社区监督员) of GodNet/VITAS, a Chinese-language DDoS-for-hire hacking group. We also found that a device used by HangHang2017, one of the group's members, was infected with infostealer malware in 2023, leaving numerous traces. The data exfiltrated by the malware includes all of the URLs, usernames, and passwords that this member used on their device to sign in to Microsoft or Oracle cloud consoles. We therefore assess that if the subscriber information held by each of these companies is examined to first identify the person behind HangHang2017, and the investigation is then expanded from there, the identity of YY520CN could be corroborated.
HangHang2017 is a member responsible for infrastructure management within the VITAS group and operated the social media accounts, email addresses, domains, and Microsoft 365 (M365) tenants listed below.
| Indicator Type | Indicator | Source |
|---|---|---|
| Social media account | HangHang2017 | Telegram profile |
| Social media account | https://facebook[.]com/oswald.low | GitHub |
| Social media account | https://github[.]com/oswaldlow | GitHub |
jinhanglow87@gmail[.]com | 2023 infostealer logs, GitHub | |
jinhanglow87@popcorn745[.]ga | 2023 infostealer logs | |
popcorn093@popcorn745.onmicrosoft[.]com | 2023 infostealer logs | |
| Domain | demonsword[.]top | 2023 infostealer logs |
| Domain | popcorn745[.]ga | 2023 infostealer logs |
| M365 tenant | popcorn745.onmicrosoft[.]com | 2023 infostealer logs |
| M365 tenant | xs1001.onmicrosoft[.]com | 2023 infostealer logs |
We assess that the GodNet/VITAS group is organized as follows:
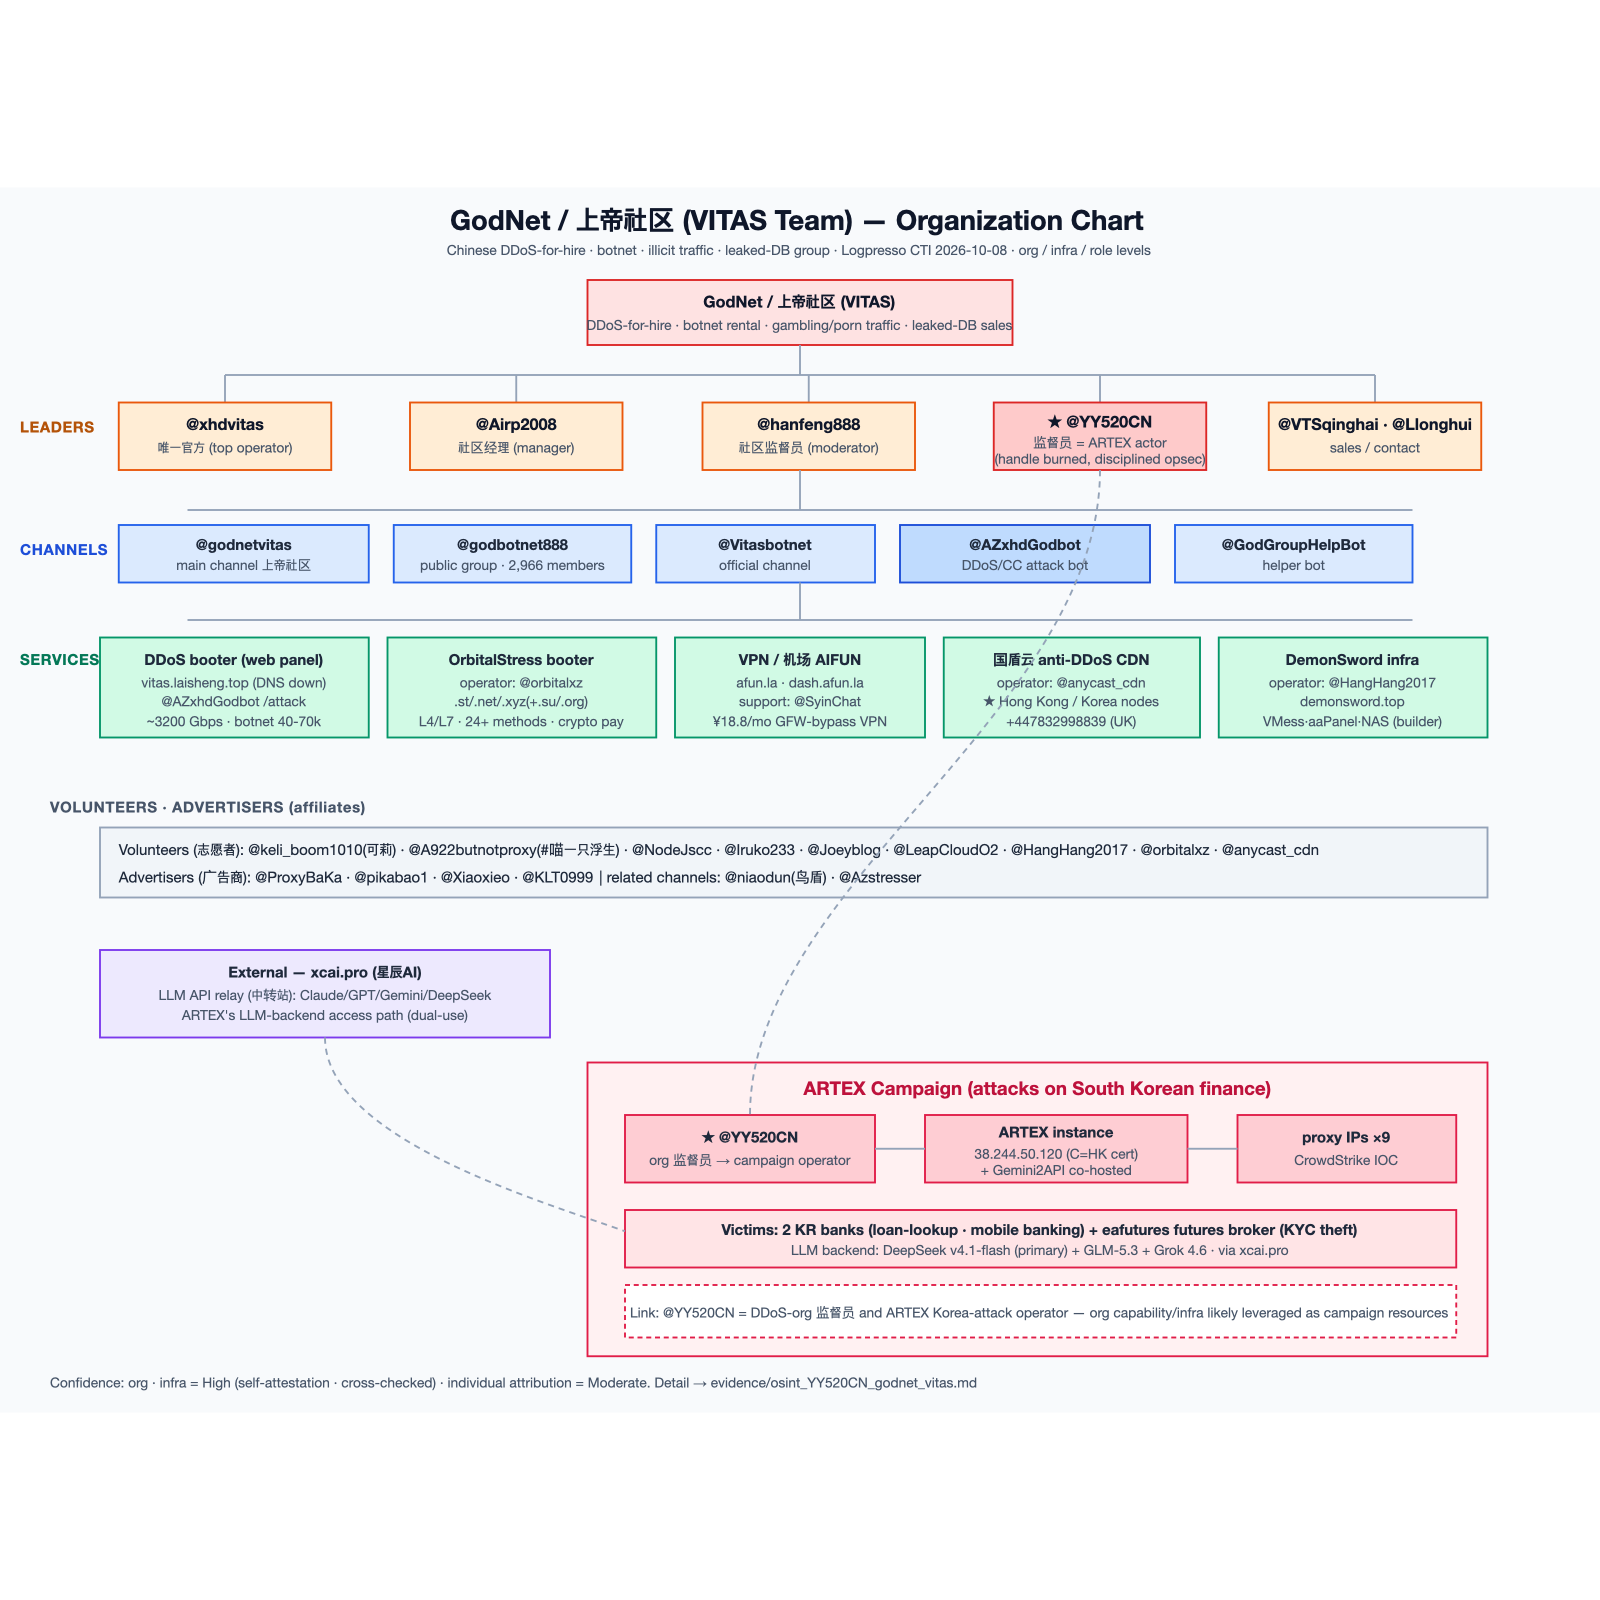
The sections below describe how we identified the group's members.
Reviewing the CrowdStrike Report
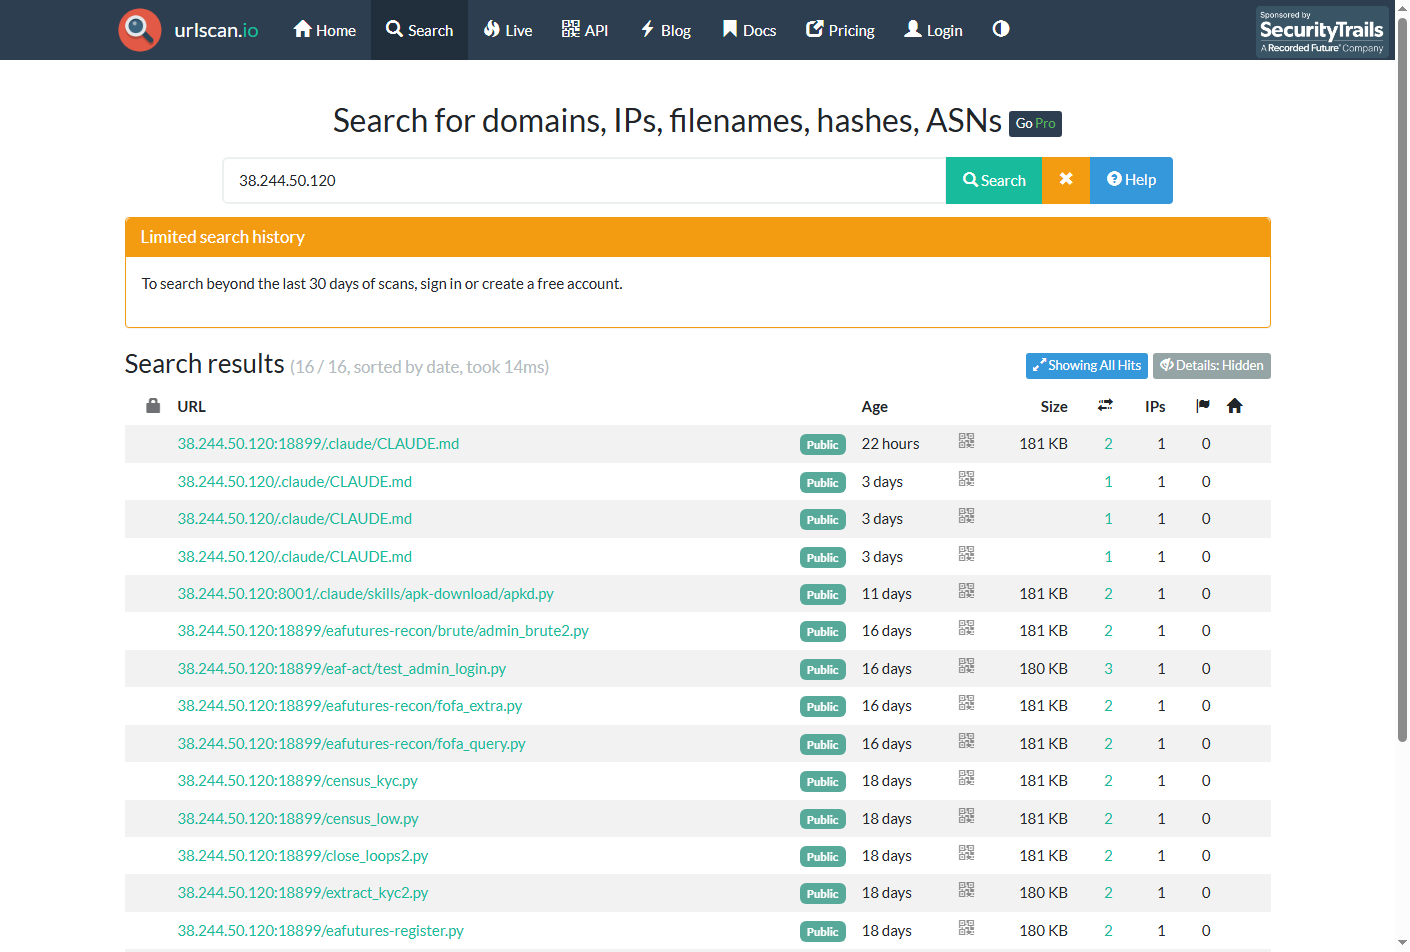
Pivoting from the IP address 38.244.50[.]120, an indicator of compromise, CrowdStrike found a Claude Code markdown file at http[:]//38.244.50[.]120:18899/.claude/CLAUDE.md and identified a possible threat actor from the conversation history left in this file. After CrowdStrike published its blog post, the threat actor immediately shut down the server. However, related artifacts can still be found on urlscan.io. Other artifacts, such as attempted attacks against East Asia Futures (eafutures), are also visible.
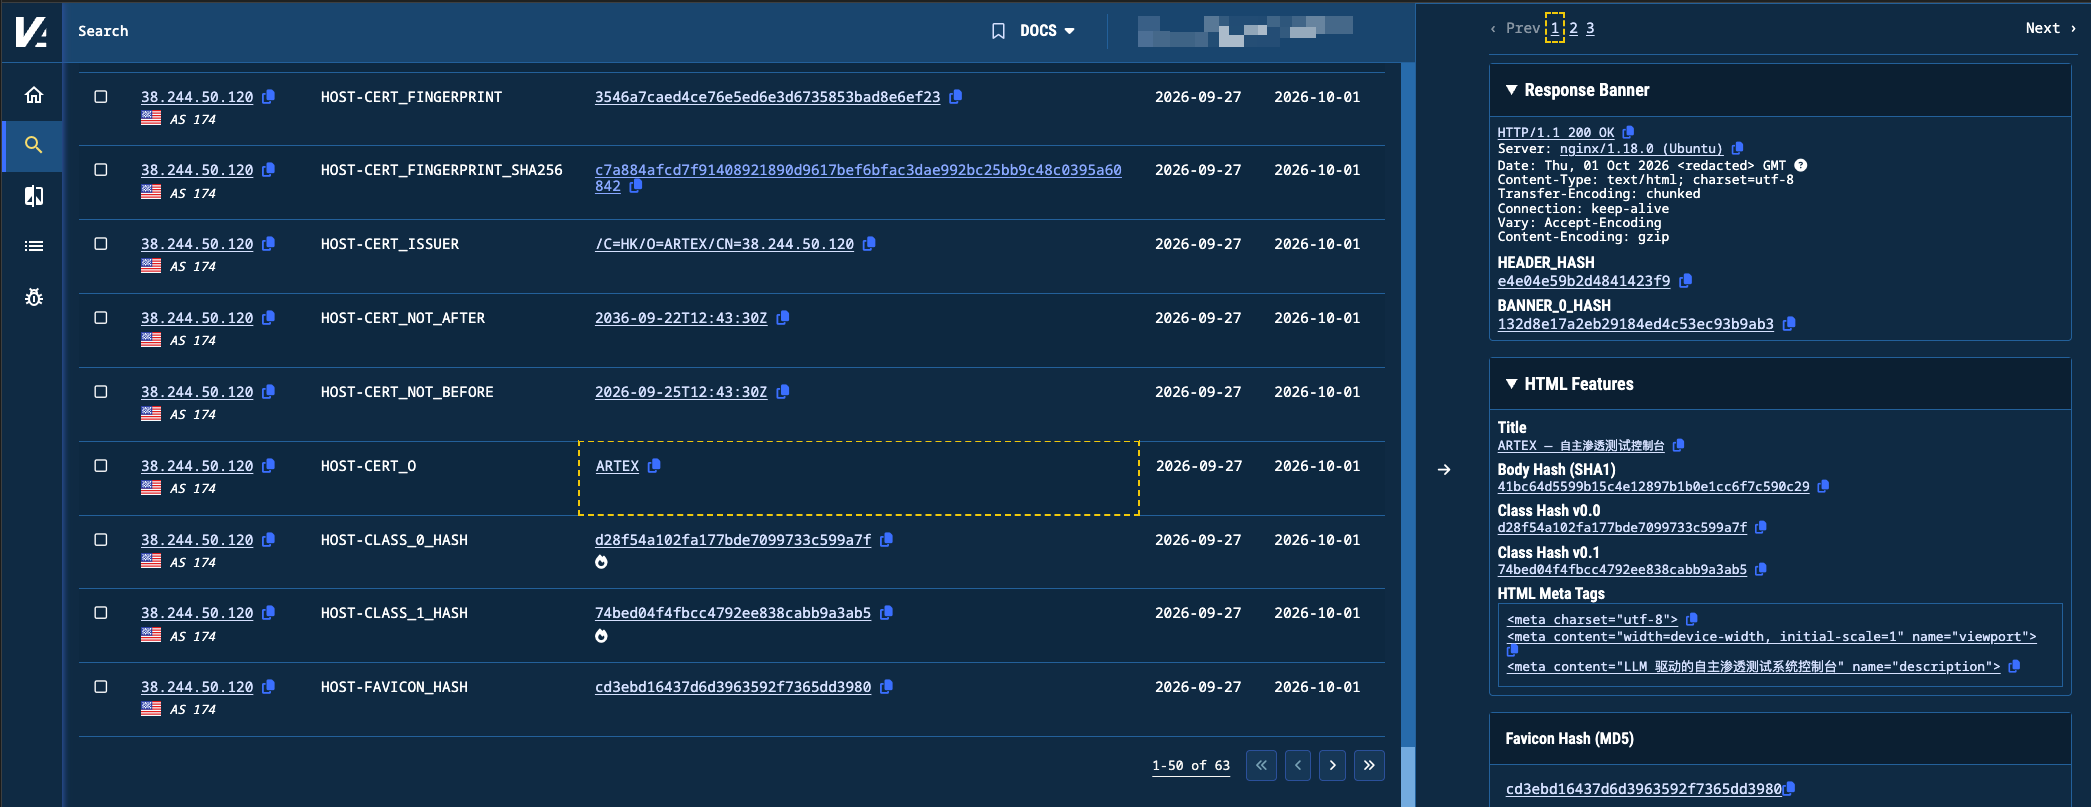
ARTEX operational artifacts on 38.244.50[.]120 can also be seen in Validin, as shown below.
Telegram Analysis
We found a post that the VITAS group published at around 8:00 AM on September 27, 2024, describing how the group is organized.
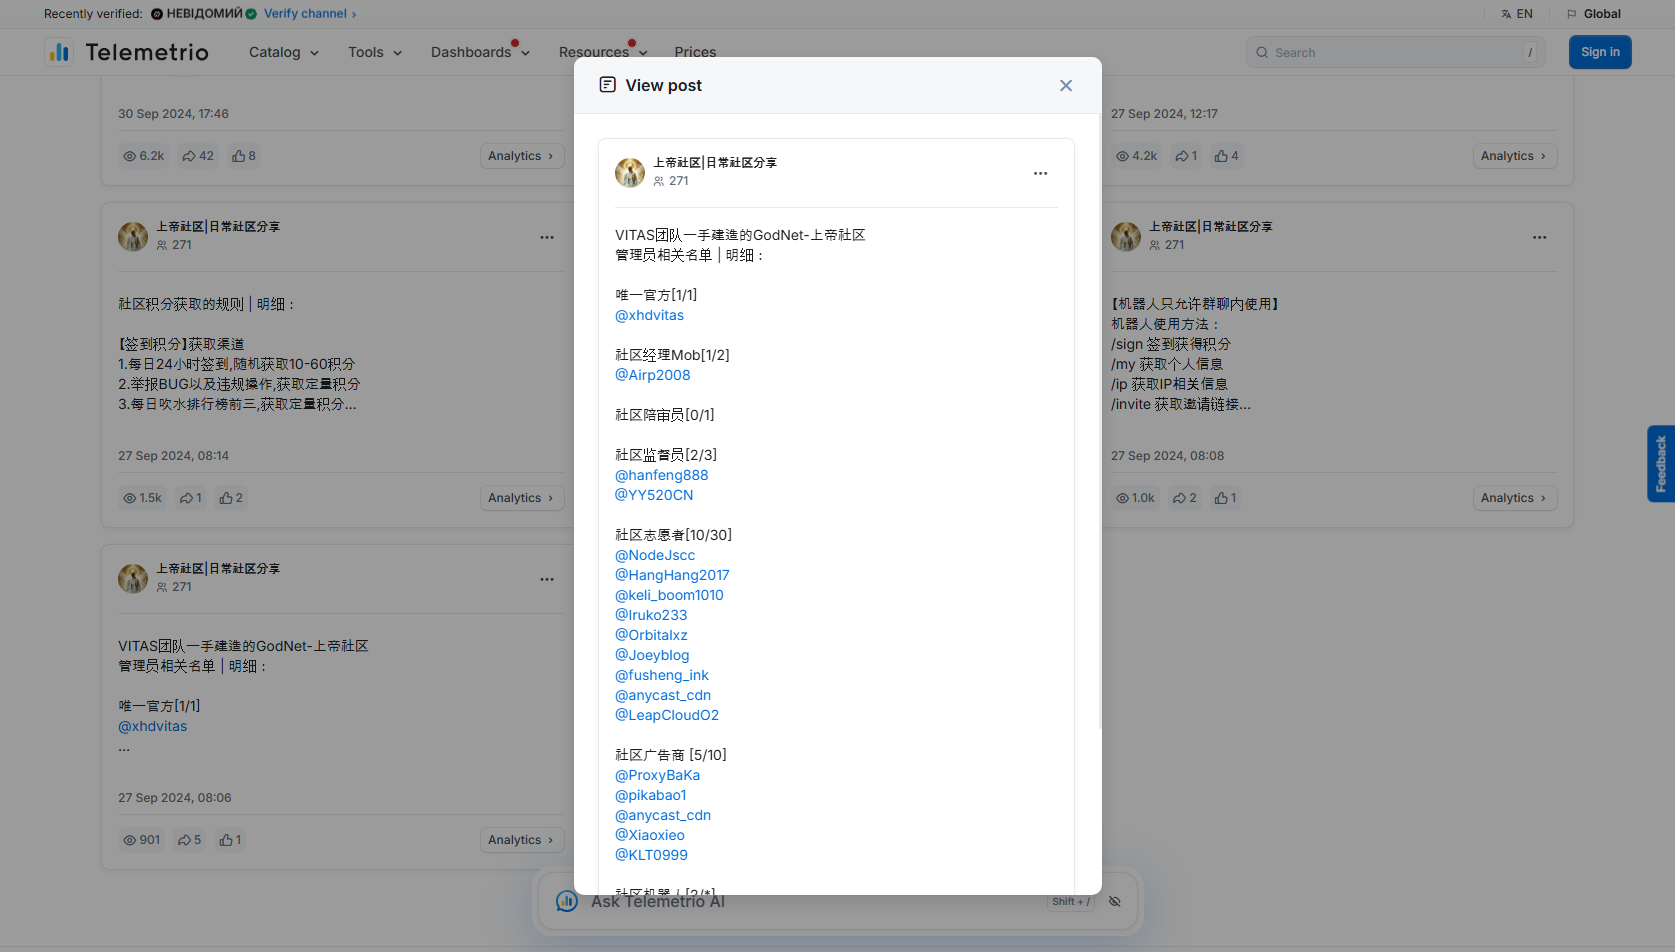
VITAS团队一手建造的GodNet-上帝社区
管理员相关名单 | 明细:

唯一官方[1/1]
@xhdvitas

社区经理Mob[1/2]
@Airp2008

社区陪审员[0/1]

社区监督员[2/3]
@hanfeng888
@YY520CN

社区志愿者[10/30]
@NodeJscc
@HangHang2017
@keli_boom1010
@Iruko233
@Orbitalxz
@Joeyblog
@fusheng_ink
@anycast_cdn
@LeapCloudO2

社区广告商 [5/10]
@ProxyBaKa
@pikabao1
@anycast_cdn
@Xiaoxieo
@KLT0999

社区机器人[2/*]
@GodGroupHelpBot {社区小帮手机器人}
@AZxhdGodbot {社区攻击机器人}

管理名单每周实时刷新,请常观察名单,谨防更替.
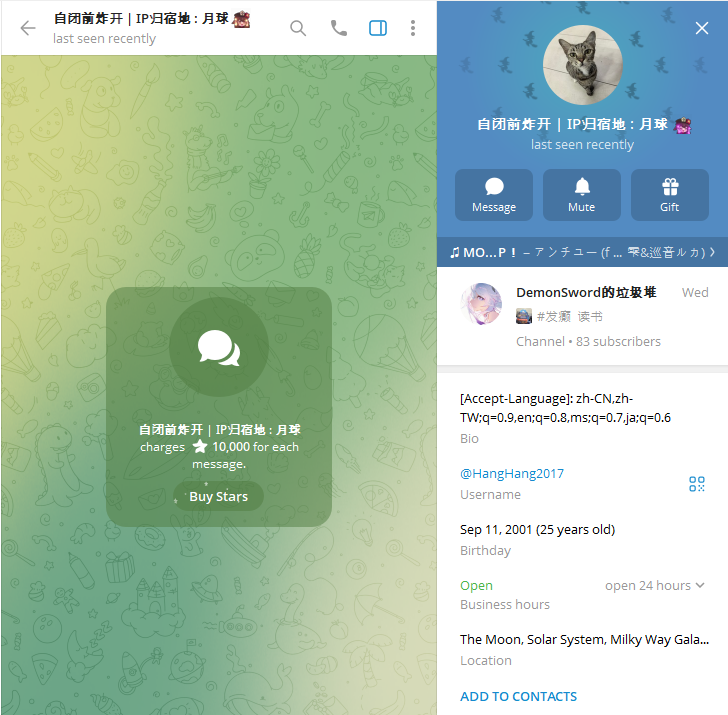
In this post, YY520CN is listed as a community supervisor (社区监督员), and HangHang2017 is listed as a community volunteer (社区志愿者). The Telegram profile of HangHang2017 is shown below.
GitHub Analysis
The code at https://github.com/oswaldlow/Auto-Wallpaper-Change/blob/Stable-V1.0/index.html shows that the owner of demonsword[.]top is linked to https://t[.]me/HangHang2017.
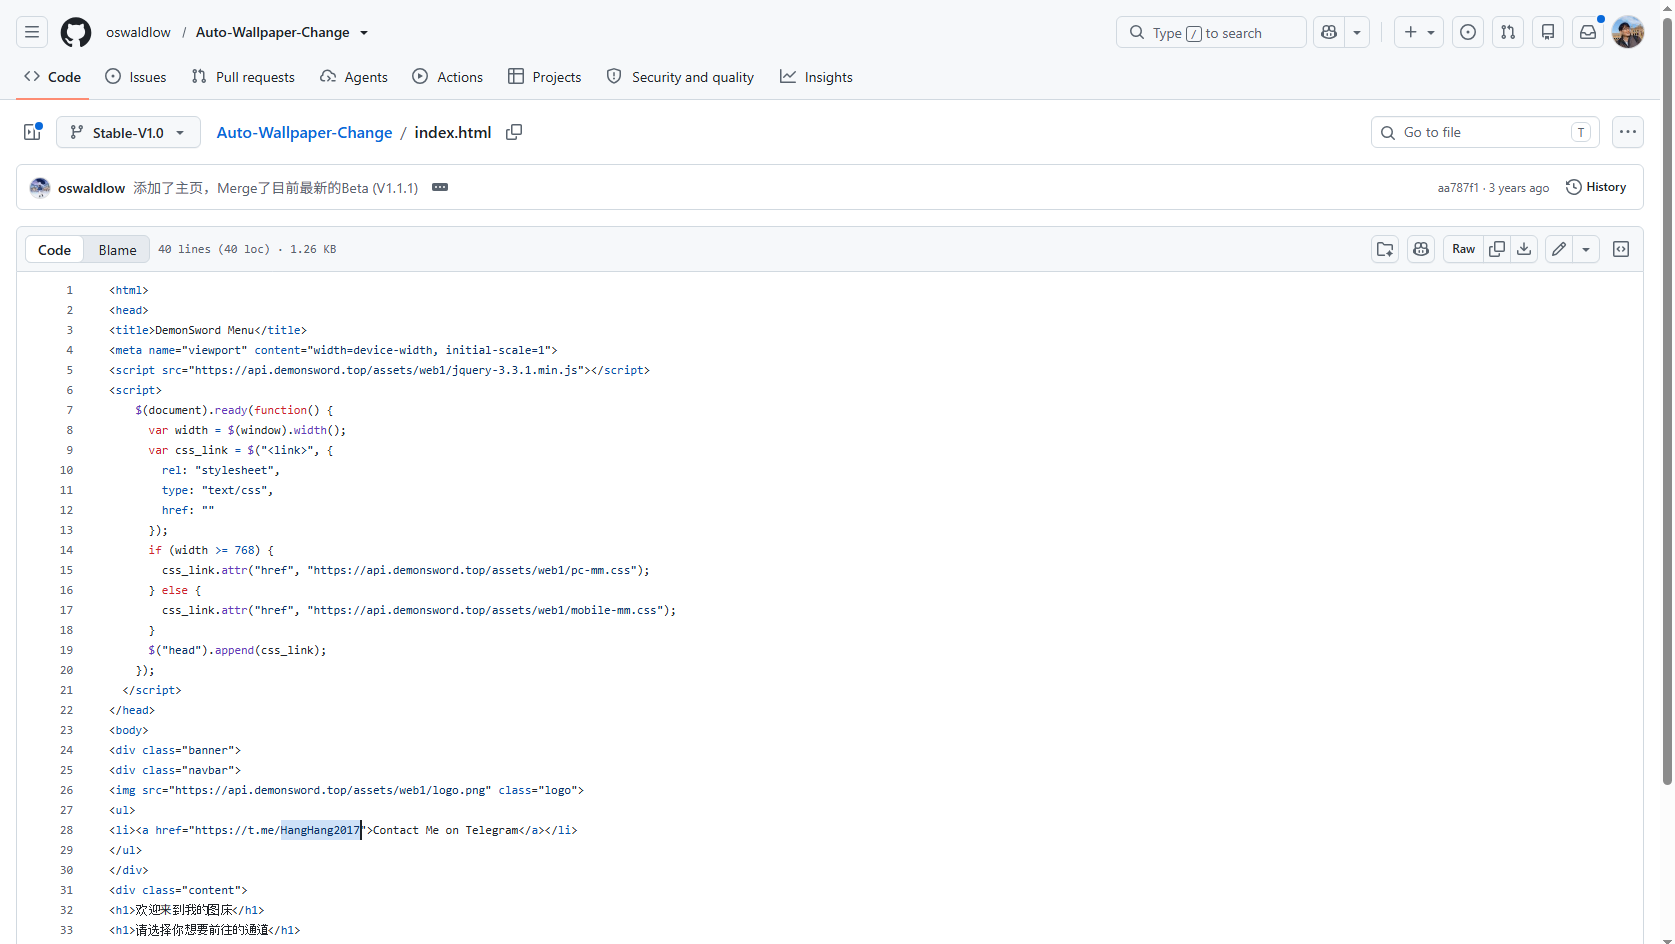
The GitHub account that committed this code is oswaldlow. Examining the commit history of all related repositories reveals the email address jinhanglow87@gmail[.]com in a commit dated March 29, 2026, as shown below.
Source: https://github.com/oswaldlow/IPQuality/commit/2f8b941a1105280e5629c79fc50c31389a045b33.patch
From 2f8b941a1105280e5629c79fc50c31389a045b33 Mon Sep 17 00:00:00 2001
From: DemonSword <jinhanglow87@gmail.com>
Date: Sun, 29 Mar 2026 18:01:10 +0800
Subject: [PATCH] Updated Date

---
 ip.sh | 2 +-
 1 file changed, 1 insertion(+), 1 deletion(-)

diff --git a/ip.sh b/ip.sh
index fd71fc2..31a13f0 100644
--- a/ip.sh
+++ b/ip.sh
@@ -1,5 +1,5 @@
 #!/bin/bash
-script_version="v2026-03-13"
+script_version="v2026-03-29"
 check_bash(){
 current_bash_version=$(bash --version|head -n 1|awk -F ' ' '{for (i=1; i<=NF; i++) if ($i ~ /^[0-9]+\.[0-9]+\.[0-9]+/) {print $i; exit}}'|cut -d . -f 1)
 if [ "$current_bash_version" = "0" ]||[ "$current_bash_version" = "1" ]||[ "$current_bash_version" = "2" ]||[ "$current_bash_version" = "3" ];then
Infostealer Log Analysis
After infecting a device, an infostealer exfiltrates all credentials and other authentication data stored in the device's web browsers to an attacker-controlled server. Logpresso has been collecting infostealer logs posted on the dark web for an extended period. By searching for the email address jinhanglow87@gmail[.]com obtained in the previous step, we found authentication records leaked in 2023, as shown below.
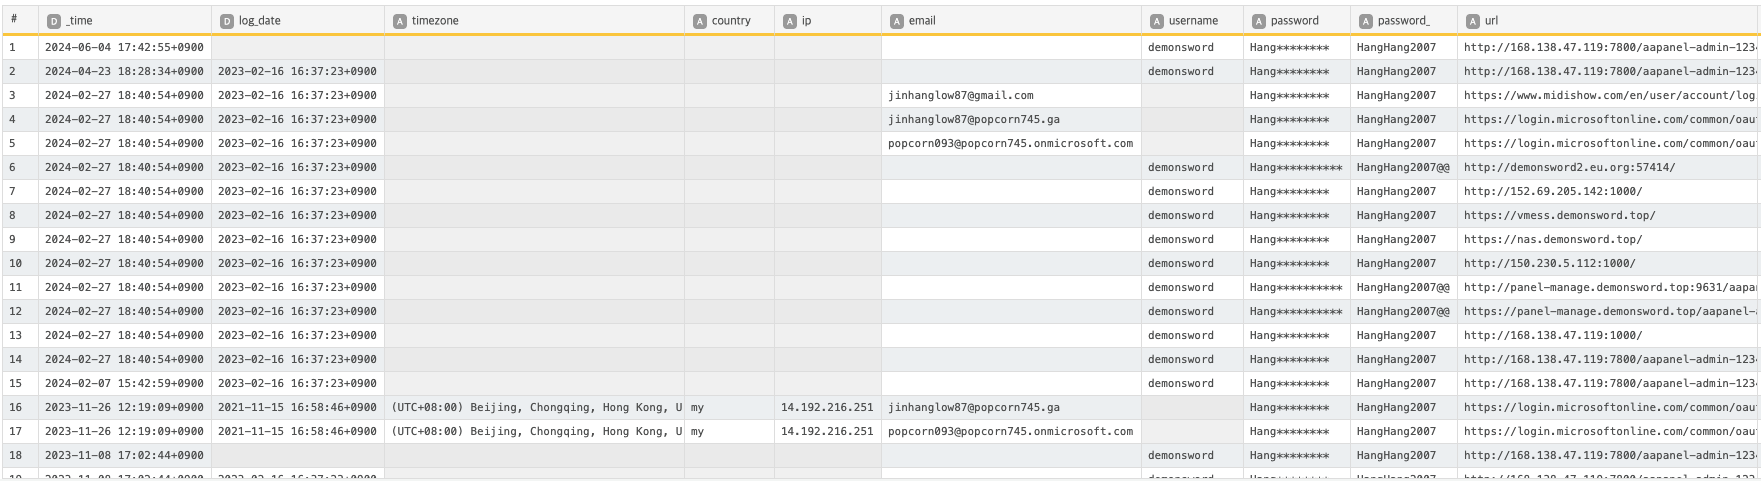
From these records, we can infer that HangHang2017, a member of the VITAS group, used V2Ray and its VMess protocol to anonymize internet traffic. The records also confirm that this member used aaPanel's WordPress Toolkit to manage websites and operated the popcorn745.onmicrosoft[.]com tenant with a separate domain, popcorn745[.]ga, connected to it.
Conclusion
This analysis builds on the report published by CrowdStrike and cross-references Telegram, GitHub commit history, and infostealer logs. Based on the results, we consider it difficult to conclude definitively that a lone individual led the breaches of South Korean financial institutions.
Logpresso confirmed two key points. First, the YY520CN account was one of the community administrators of GodNet/VITAS, a DDoS-for-hire hacking group. Second, through infostealer logs, we identified the email addresses, domains, and M365 tenant information linked to HangHang2017, a member of the same group.
Matching these records against the subscriber information held by cloud service providers should therefore make it possible to identify the actual operator of the HangHang2017 account and, using that as a starting point, to establish the identity of YY520CN as well.
Regardless of whether the identity is confirmed, the steps security teams should take are clear. CrowdStrike assessed that this attack did not involve new techniques; instead, AI was used to increase its speed and scale. The threat actor targeted externally exposed ancillary services, such as loan inquiry and mobile work-support services, rather than core systems. Security teams should bring every externally accessible system into the scope of their security reviews, even if it is not customer-facing. They should also check whether lookup authorization is properly verified even after login and whether anomalous repeated queries are being detected.